
PostgreSQL Hit by 12-Year-Old Vulnerability Allowing Server Takeover
PostGREShell (CVE-2026-6471) is a 12-year-old PostgreSQL flaw that lets low-privileged attackers execute code and take over servers. Cyera researchers found a severe PostgreSQL vulnerability, dubbed PostGREShell and tracked as CVE-2026-6471 (CVSS score of 7.2). Present in releases dating back to 2014, the flaw can be exploited by attackers with low-level replication access to execute code, […]
 Pierluigi Paganini
 September 04, 2026
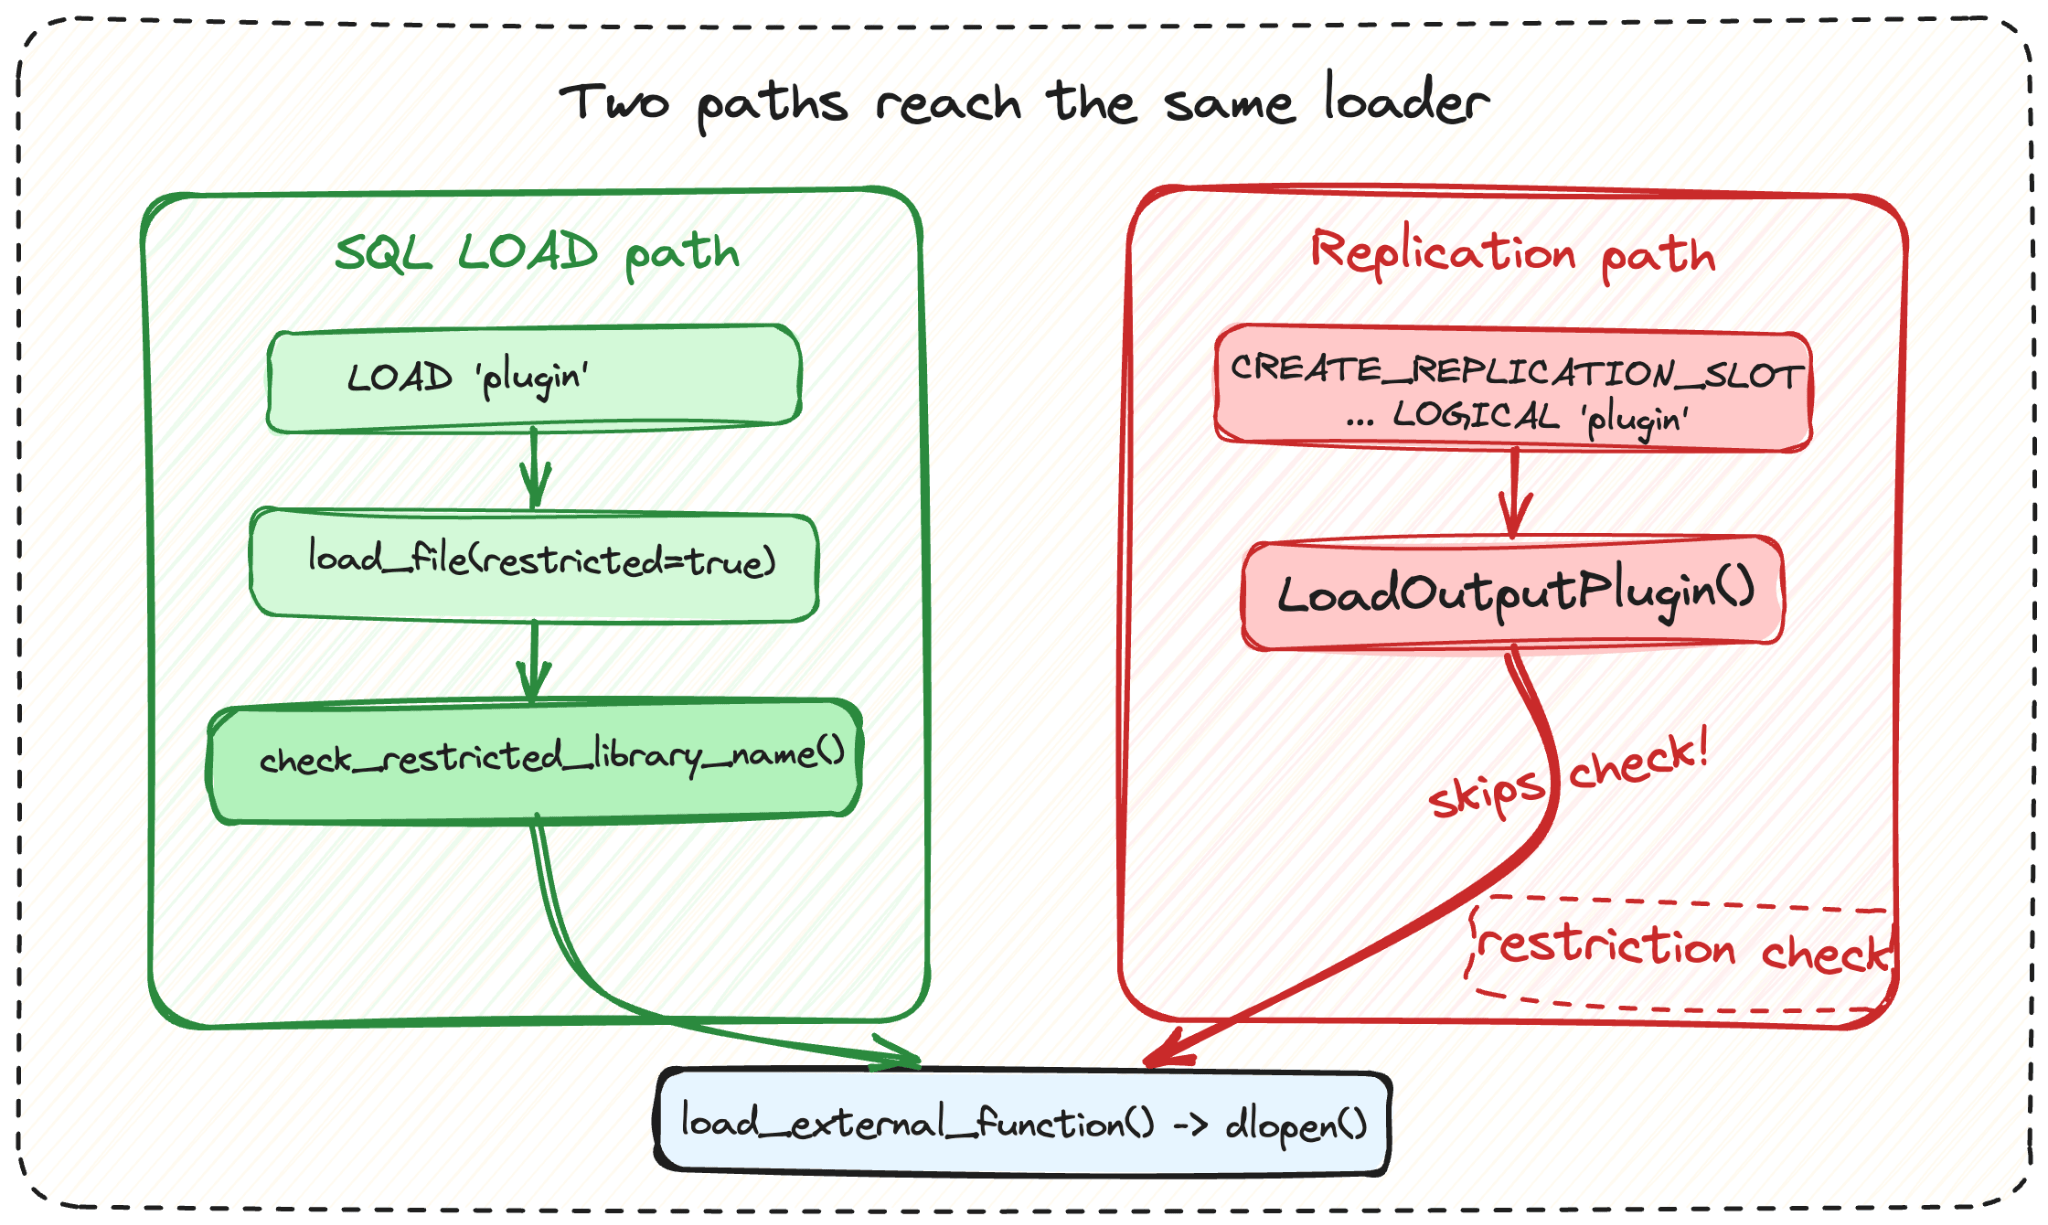
Cyera researchers found a severe PostgreSQL vulnerability, dubbed PostGREShell and tracked as CVE-2026-6471 (CVSS score of 7.2). Present in releases dating back to 2014, the flaw can be exploited by attackers with low-level replication access to execute code, escalate privileges and gain permanent superuser access.
Related breach coverage
- 12-Year-Old PostgreSQL Vulnerability Enables Database, Server Takeover2026-09-04
Dubbed PostGREShell, CVE-2026-6471 turns low-level replication access into code execution, permanent superuser privileges and a persistent database backdoor. The post 12-Year-Old PostgreSQL Vulnerability Enables Database, Server Takeover appeared first on SecurityWeek.
- Hackers Target Langflow in CVE-2026-0768 Attacks2026-09-02
Hackers are exploiting a critical Langflow flaw that lets unauthenticated attackers remotely execute Python code on vulnerable systems. Hackers have started exploiting a critical vulnerability, tracked as CVE-2026-0768 (CVSS score of 9.8), in the AI-focused low-code platform Langflow. The flaw affects the code validator in Langflow’s custom component editor, it impacts all Langflow versions up […]
- Cisco Fixed Critical RCE in Nexus 9000 Series Switches2026-09-03
Cisco patched a critical Nexus 9000 vulnerability, CVE-2026-20212, allowing unauthenticated remote root code execution. Cisco has released patches for a critical flaw, tracked as tracked as CVE-2026-20212 (CVSS score of 9.8) in 10 Silicon One-based Nexus 9000 switches. The vulnerability could let an unauthenticated remote attacker execute code with root privileges. Cisco’s Technical Assistance Center […]
- Cisco Warns of Ongoing Exploitation of Critical Email Gateway Zero-Day2026-09-15
Cisco warns of a critical zero-day in Secure Email Gateway, exploited in the wild to gain root access through malicious emails. Cisco disclosed a critical zero-day, tracked as CVE-2026-76461 (CVSS score of 9.8), affecting Secure Email Gateway appliances. The flaw can be exploited remotely without authentication. Attackers can send specially crafted emails containing malicious SQL […]